PHP Vulnerability Exploit Uses AI to Identify Hidden Memory-Management Problem
A serious security vulnerability was discovered in PHP's core engine, potentially allowing attackers to execute malicious code on vulnerable servers without logging in. Researchers used Artificial Intelligence (AI) to identify a hidden memory-management problem that traditional security testing had missed.
A serious security vulnerability was discovered in PHP's core engine, potentially allowing attackers to execute malicious code on vulnerable servers without logging in. The interesting part is how researchers used Artificial Intelligence (AI) to identify a hidden memory-management problem that traditional security testing had missed.
This discovery highlights three important topics: how memory corruption works, why older security testing methods can miss certain bugs, and how AI is changing vulnerability research.
1. Why Is This PHP Vulnerability So Serious?
PHP is used by millions of websites and applications. Before a PHP application can process a request, the PHP engine must first receive and understand the incoming data.
This means a vulnerability inside PHP's core engine can affect applications before their own security checks even begin.
Examples of software built on PHP include:
- CMS: WordPress, Drupal and Joomla.
- Frameworks: Laravel.
- Self-hosted tools: Nextcloud and phpMyAdmin.
- Server environments: LAMP and WAMP stacks.
If the vulnerability is triggered while PHP is processing an HTTP request, application-level protections such as login checks and input validation may never get a chance to run.
2. How Does the Exploit Work?
The main problem involves a memory error called Use-After-Free (UAF).
Programs written in C often manage memory manually. They allocate memory when needed and release it when the data is no longer required.
A Use-After-Free error happens when a program continues using memory after it has already been released. Another operation may reuse that same memory, causing unexpected data changes or potentially allowing an attacker to control program execution.
How Researchers Found the Problem
Researchers first investigated an out-of-memory error during PHP's request processing. They noticed that PHP could release session memory without properly clearing references pointing to it.
They then described the problem as a reusable pattern and used AI models to search other parts of the PHP codebase for similar mistakes.
This investigation highlighted another vulnerable
code path involving PHP's legacy
session.upload_progress feature.
The Two-Request Exploit
The reported exploit involves two consecutive HTTP requests.
Request 1: Creating the memory problem
- An attacker sends a specially crafted file-upload request.
- The request triggers a memory allocation failure.
- PHP releases session memory but leaves some references pointing to the released memory.
Request 2: Using the released memory
- The attacker sends another file-upload request.
- PHP attempts to access the previous session data.
- It uses references that point to memory that has already been released.
- This can lead to memory corruption and potentially remote code execution.
How Can This Lead to Code Execution?
Think of memory as a storage area divided into small sections. Different program objects use these sections to store information.
If released memory is reused by another object, an attacker may be able to overwrite important information, including pointers that control which functions the program executes.
Under the right conditions, this memory corruption can provide arbitrary memory read/write capabilities and eventually lead to Remote Code Execution (RCE).
3. Why Did Traditional Security Testing Miss It?
One of the most interesting aspects of this discovery is the difference between traditional fuzzing and AI-assisted code analysis.
What Is Fuzzing?
Fuzzing is an automated security-testing technique. It sends large numbers of modified inputs to software to find unexpected crashes, errors, and memory problems.
It is particularly effective at finding problems such as:
- Buffer overflows.
- Out-of-bounds memory access.
- Unexpected input-handling errors.
- Integer-related memory problems.
Where Traditional Fuzzing Struggles
Some memory bugs do not happen in a single operation. They depend on a sequence of events occurring over time.
For example:
- A program allocates memory.
- An unexpected error interrupts normal processing.
- Memory is released, but old references remain.
- A later request accesses those references.
This makes certain Use-After-Free vulnerabilities harder to discover through ordinary single-execution fuzzing.
How AI Helped Find the Vulnerability
Researchers created a structured description of the original memory-management failure and used Large Language Models (LLMs) to search the wider PHP codebase for similar patterns.
Instead of simply testing random inputs, the AI examined how different parts of the code handled memory, errors, and cleanup operations.
This helped researchers identify similar problems in older PHP code that had remained unnoticed for years.
| Area | Traditional Fuzzing | AI Code Analysis |
|---|---|---|
| Main focus | Input-related errors | Logical code patterns |
| Memory issues | Buffer and boundary errors | Cleanup and dangling references |
| Approach | Tests modified inputs | Examines code relationships |
| Best use | Finding execution failures | Finding repeated logic mistakes |
AI does not replace fuzzing. Both techniques can complement each other: fuzzing tests how software behaves, while AI-assisted analysis can help identify suspicious patterns in the source code.
4. Patching the Vulnerability and Remaining Risks
Following the discovery, PHP developers released security updates for affected branches. However, testing showed that fixing complex memory-management problems can require more than one patch.
Why Patch Testing Matters
Researchers reported that some initial patched builds still triggered memory errors during testing with AddressSanitizer (ASan).
ASan is a development tool that helps detect memory problems such as:
- Use-After-Free errors.
- Double-free errors.
- Out-of-bounds memory access.
This shows why security patches must be tested against different execution paths rather than assuming that the first fix resolves every related issue.
What Should Website Owners Do?
- Update PHP: Install the appropriate official security updates for your PHP branch.
- Check your server: Identify which PHP version your website is actually running.
- Review upload functionality: Pay attention to applications handling multipart file uploads.
- Do not rely only on WAFs: A Web Application Firewall cannot guarantee protection against every vulnerability inside the PHP runtime.
The Bigger Lesson: Memory-Safe Programming
This incident also highlights the benefits of memory-safe programming languages.
Languages such as Rust use ownership and borrowing rules to prevent many common memory errors during compilation. This helps eliminate entire categories of problems, including many Use-After-Free conditions.
As AI-assisted security research improves, developers should also expect more attention on older C and C++ software that powers critical internet infrastructure.
Conclusion
This PHP vulnerability demonstrates how a small memory management mistake can create serious security risks across a large software ecosystem.
More importantly, it shows how AI can help security researchers identify patterns that traditional automated testing may overlook.
The future of software security will likely depend on combining traditional testing, AI-assisted code analysis, memory-safe programming, and thorough patch verification.
On This Page
- 1. Why Is This PHP Vulnerability So Serious?
- 2. How Does the Exploit Work?
- How Researchers Found the Problem
- The Two-Request Exploit
- Request 1: Creating the memory problem
- Request 2: Using the released memory
- How Can This Lead to Code Execution?
- 3. Why Did Traditional Security Testing Miss It?
- What Is Fuzzing?
- Where Traditional Fuzzing Struggles
- How AI Helped Find the Vulnerability
- 4. Patching the Vulnerability and Remaining Risks
- Why Patch Testing Matters
- What Should Website Owners Do?
- The Bigger Lesson: Memory-Safe Programming
- Conclusion

Subscribe to One2Tech Insights
Stay updated with our latest development and tech guides.
More from Tech News
View all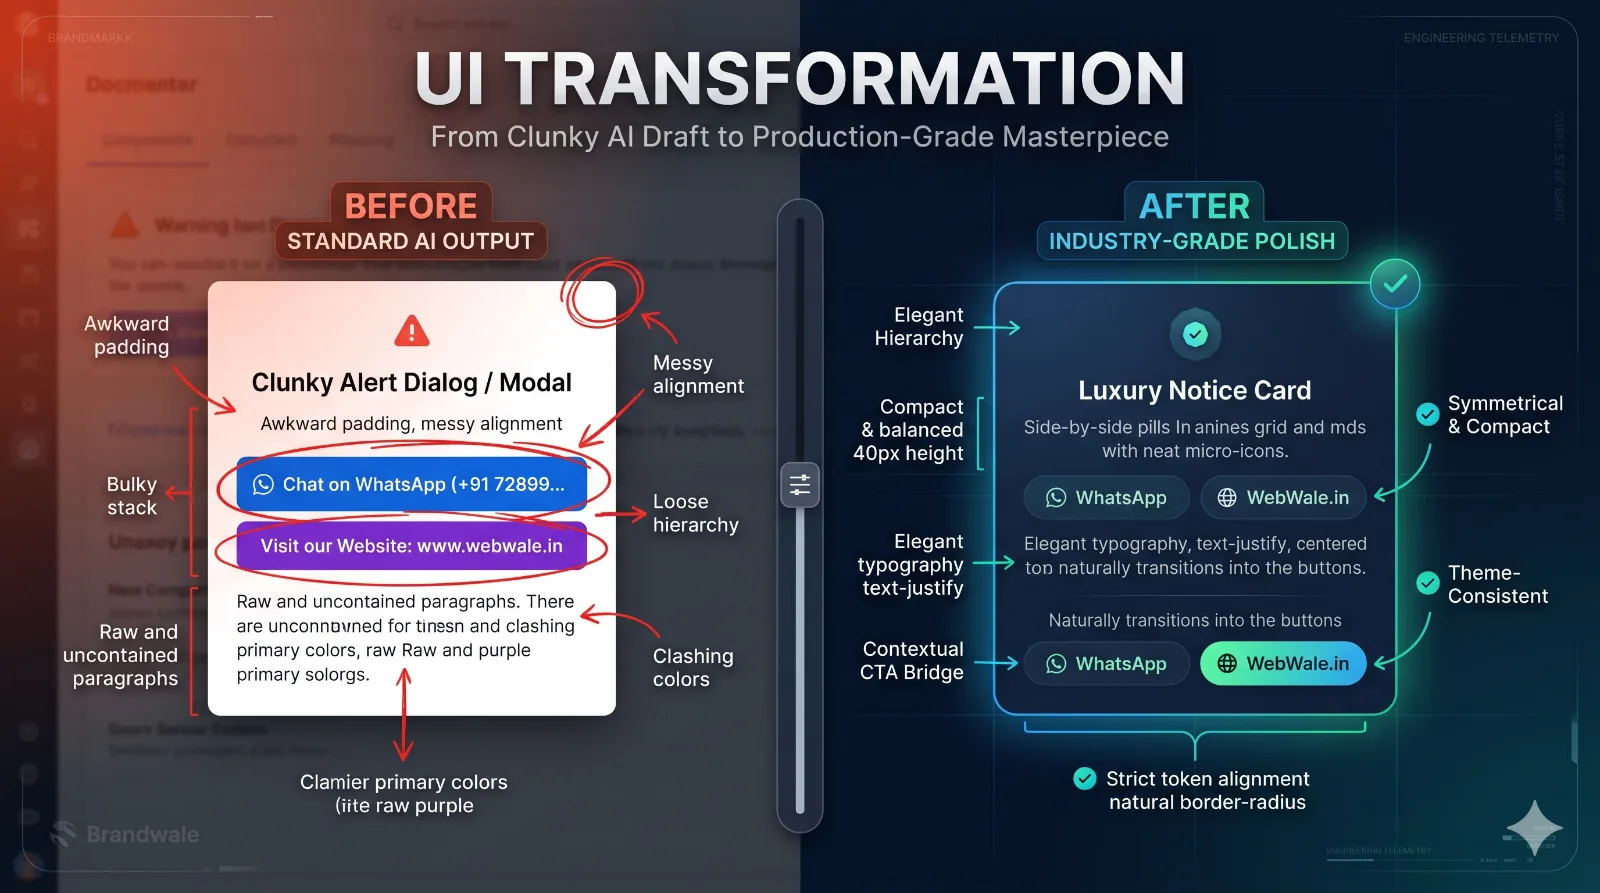
Transforming AI-Generated UI Components into Industry-Grade Masterpieces
Discover the 5 pillars of observer-level UI engineering that bridge the gap between amateur AI output and production-grade craftsmanship.
How to Turn Your Android Phone into a Local Shared Drive Using Wi-Fi Hotspot
You can turn your Android phone into a local file-sharing server and access a specific folder from Windows, Mac, or other phones connected to its Wi-Fi hotspot.